Summary
This article examines DoppelCart, a large-scale shopping fraud network encompassing approximately 261,700 suspected domains identified by Recorded Future. These fraudulent storefronts copy legitimate retailers’ branding and product listings to deceive shoppers into disclosing personal and payment information, with some also capturing bank-issued verification codes to authorize fraudulent transactions. This research highlights the network’s widespread impersonation of US brands, evolving hosting infrastructure, and use of shared payment-routing configurations and the Medusa e-commerce platform. With approximately 40% of observed DoppelCart websites remaining active, understanding these patterns can help retailers identify brand impersonation and help consumers recognize fraudulent shopping sites.
Background
In September 2026, German cybersecurity company Nebty exposed DoppelCart, a large-scale online shopping fraud network with over 119,000 websites. The fraudulent storefronts copy legitimate retailers’ product listings, images, and descriptions to deceive shoppers into entering payment information.
Researchers identified shared website designs, code, and infrastructure across thousands of suspicious storefronts, eventually linking the domains to the DoppelCart cluster. Most websites used .shop web addresses, and many advertised steep discounts, including offers of 65% off, to attract shoppers. Although the websites shared technical characteristics, Nebty cautioned that the findings did not establish whether a single criminal organization operated the entire network.
According to subsequent reporting by Malwarebytes and BleepingComputer, fraudulent checkout pages transmit shoppers’ personal and payment information to attacker-controlled servers in real time. Some also capture one-time verification codes issued by banks, potentially allowing criminals to authorize transactions while victims believe they are completing legitimate purchases.
Domains Discovered by Recorded Future
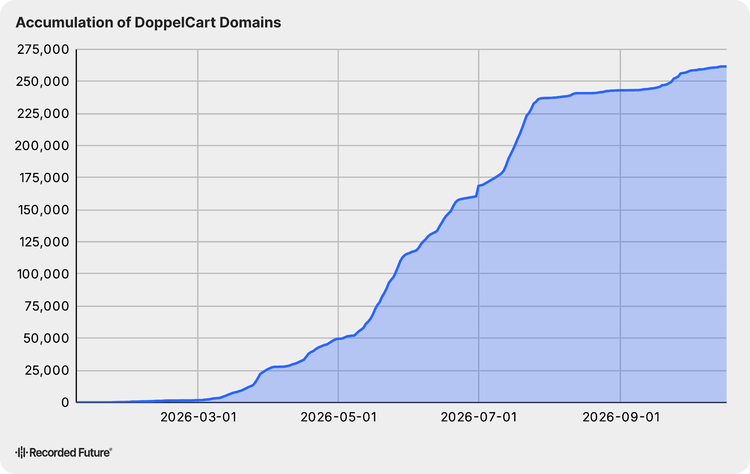
Primarily between March and October 2026, Recorded Future used proprietary methods to identify approximately 261,700 unique apex domains that are likely part of the DoppelCart fraud network. Based on our collections, a few thousand DoppelCart detections began appearing in January 2026 and increased during March. Our detections peaked during the months of June and July, with a sharp drop-off in new hosts starting in August.
While new host growth mostly plateaued thereafter, a drop-off in new detections is not necessarily an indicator that operations are abating. More likely, it reflects that many previously registered domains remain active, and that operators may have shifted their focus to maintaining existing infrastructure rather than expanding it. Based on data from Recorded Future® Web Scans, approximately 40% of suspect websites in this cluster observed prior to October 17, 2026, remain active.
Source: RecordedFuture
Source Link: https://www.recordedfuture.com/blog/doppelcart-fraud-network-grows-domains